JavaScript · A practical introduction
JavaScript widget boundaries
A small API and an enforced boundary are different things. Follow the objects, permissions and browser mechanisms involved.
Read the article
Explore the historic ADsafe JavaScript subset, widget structure and DOM interface through independent, newly written guides.
What should a third-party widget be allowed to read or change? ADsafe explored a restricted language and a limited interface to the page. This independent reference revisits the historic project associated with Douglas Crockford.
How did language checks and the runtime work together? Start with the widget model and its DOM interface, then compare that design with browser isolation today.
// Illustrative historical pattern
ADSAFE.go('DEMO_', function (dom) {
  'use strict';
  dom.q('#DEMO_MESSAGE').value('Started.');
});
Conceptual example, not a validated widget.
Read the historical template →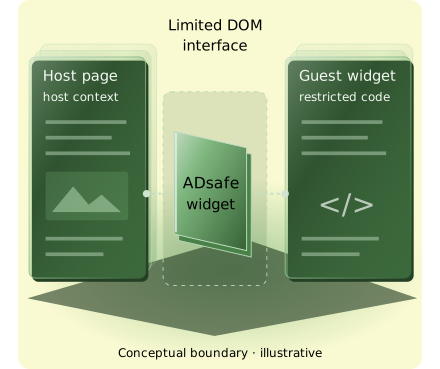
// Illustrative historical pattern
ADSAFE.go('DEMO_', function (dom) {
  'use strict';
  dom.q('#DEMO_MESSAGE')
     .value('Started.');
});

// See the full widget template.Enter a title or topic.
Learn how a restricted language limited guest code. Follow its controlled interface to the page.
Understand the boundary
How the host, HTML fragment and guest code fit together.
Selections, bunch objects and a mediated view of the document.
Read the historical implementation with its original notice.
JavaScript · A practical introduction
A small API and an enforced boundary are different things. Follow the objects, permissions and browser mechanisms involved.
Read the articleRead the historical ADsafe workflow: the JavaScript subset, a DIV wrapper, shared ID prefixes, validation and approved libraries.
Reference for ADSAFE.go, id, lib, get and set, DOM queries, bunch objects, events and restricted names, checked against the bundled runtime.
Understand ADsafe’s trusted host, restricted language, mediated DOM, capability leakage, prototype assumptions and historical limitations.
Walk through a bounded text update, an event handler and local widget state, then read the Roman, Bats and Sudoku examples with their limits in view.
Learn the object-capability idea behind ADsafe and compare its historical subset with Caja, SES compartments and browser sandboxed iframes.
A source-led account of Douglas Crockford’s historical ADsafe project, its original documentation, the bundled runtime and this independent edition.
Answers about ADsafe validation, guest widgets, DIV identifiers, approved libraries, dynamic properties, events and the limits of this historical reference.
Definitions of ADsafe terms: guest, host, widget, capability, verifier, bunch, hunters, peckers, mediated DOM, library and interceptor.